Permissions and security reporting

Kruvo works with your files and tools. Report faults that bypass approvals, expose secrets or allow tools to act outside their permitted scope.

Report a vulnerability

Kruvo 0.3.4 interface · demonstration data
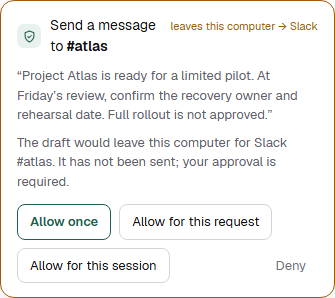
Detail of the Kruvo 0.3.4 desktop interface with demonstration data; not a mobile app.
Kruvo 0.3.4 desktop interface detail with demonstration data and simulated Slack. No model run, message sent or external action; not a mobile app.

Report a vulnerability

Email [email protected] with the Kruvo version, operating system and reproducible steps. Do not include API keys, bot tokens or private conversation content. We acknowledge reports within three business days.

In scope

  • Approval or hard-floor bypasses.
  • Prompt injection that reaches a tool with attacker-chosen arguments.
  • Secrets exposed in logs, transcripts, artifacts or messages.
  • Path traversal, SSRF or unsafe access to the local API.
  • Interaction without consent, or outside the allowed sites and apps.
  • Installer, updater and kruvo.ai service weaknesses.

How Kruvo limits access

  • Human approval for dangerous and irreversible operations in every mode.
  • An action reviewer that blocks uncertain requests and cannot override a blocked action.
  • A circuit breaker after repeated denials.
  • A local audit record with secret redaction.
  • Signed update packages, verified by the desktop updater.

Computer use

  • Off by default: a global switch in Settings, then consent per site or app, revocable at any time.
  • Kruvo's own browser observes the computed accessibility tree; the extension reads DOM roles and attributes in an isolated world, outside the page's own JavaScript. Element identities are revalidated before action. A stale target requires another observation or human review; these checks do not guarantee that page content remains unchanged.
  • Computer actions classified as sensitive require human approval in the app in every mode. Targets that cannot be verified are treated as sensitive.
  • Blocked categories and your own blocklist apply before a request reaches the model.
  • Computer-use and hard-floor approvals stay in the desktop app. Scheduled automations do not use browser or desktop-application tools.
  • In your own browser, the extension works only in Kruvo-owned tabs: it does not read, list or photograph your other tabs. Consent, blocked-site checks and approval rules apply.
  • Screenshots go to the model provider you chose; the audit trail records actions and approvals. Pausing stops subsequent work, not operating-system or external effects already in flight.

Outside the programme

Model behaviour and upstream dependency disclosures are outside scope unless they create a specific Kruvo security impact.